Content Hub
New detections the logs you already collect could support, ranked by what they add, with the case for them in plain words for the people who approve the work.
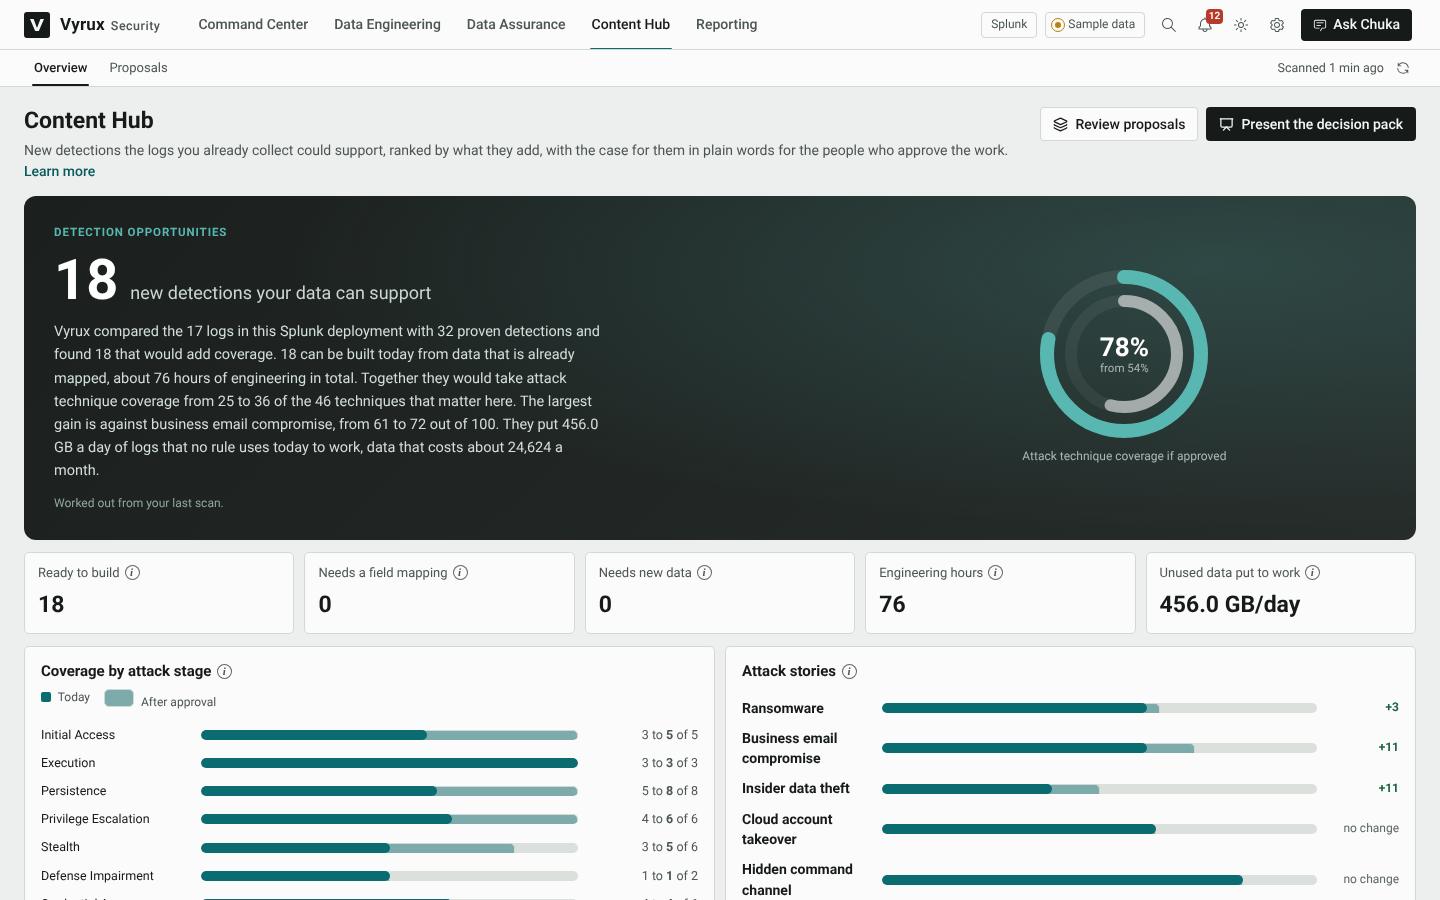
| Ready to build | The data is already mapped to the data model the detection needs |
| Needs a field mapping | The data is in Splunk, but not yet mapped |
| Needs new data | A log has to be onboarded first. The hub names which |
| Brief me with Chuka | Chuka writes a five sentence briefing for a CISO from the same numbers |
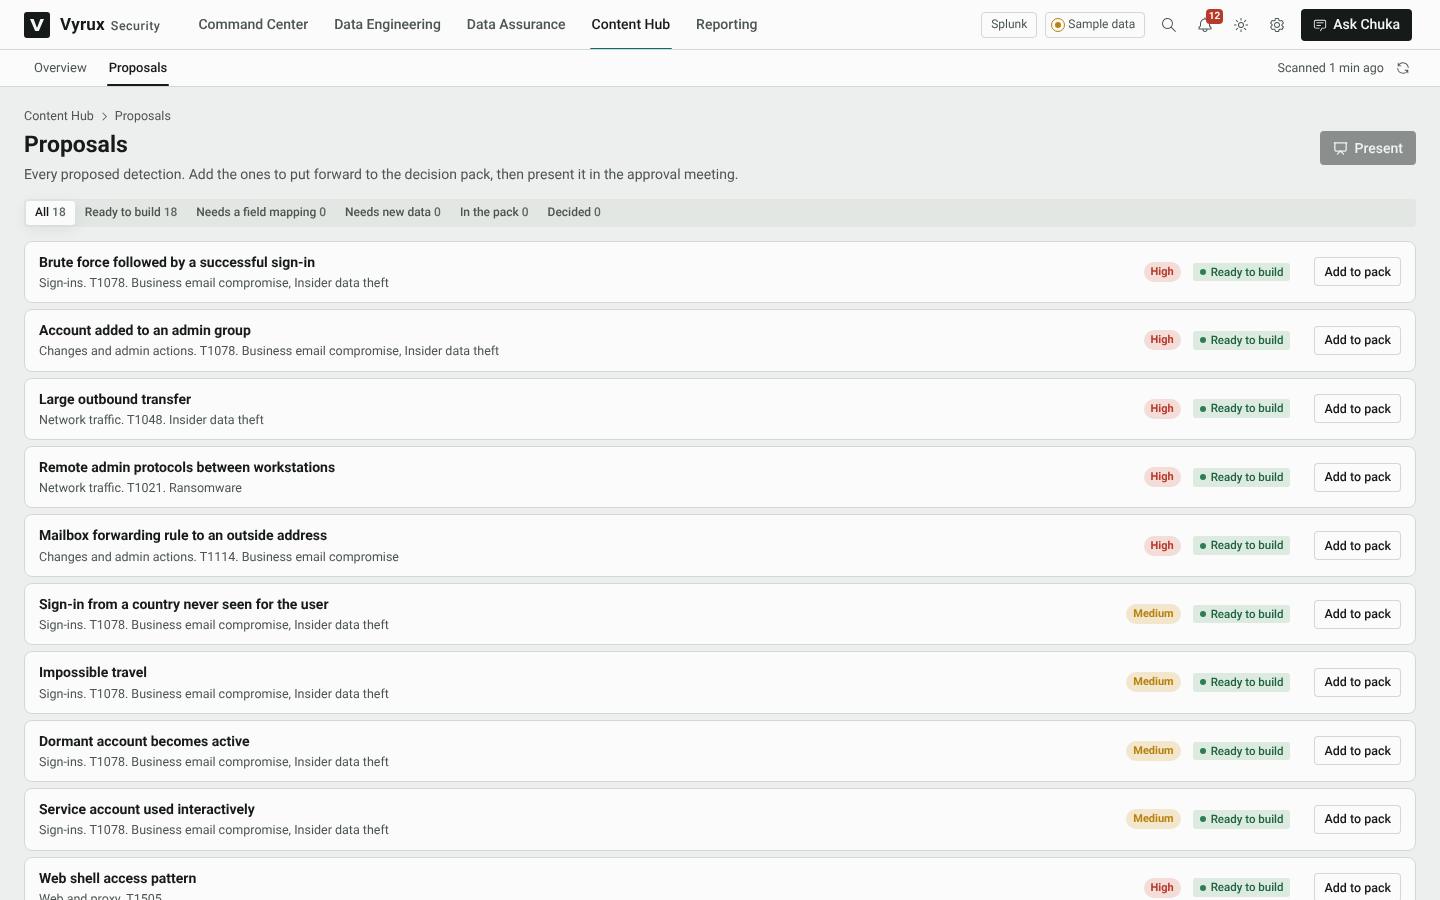
Proposals
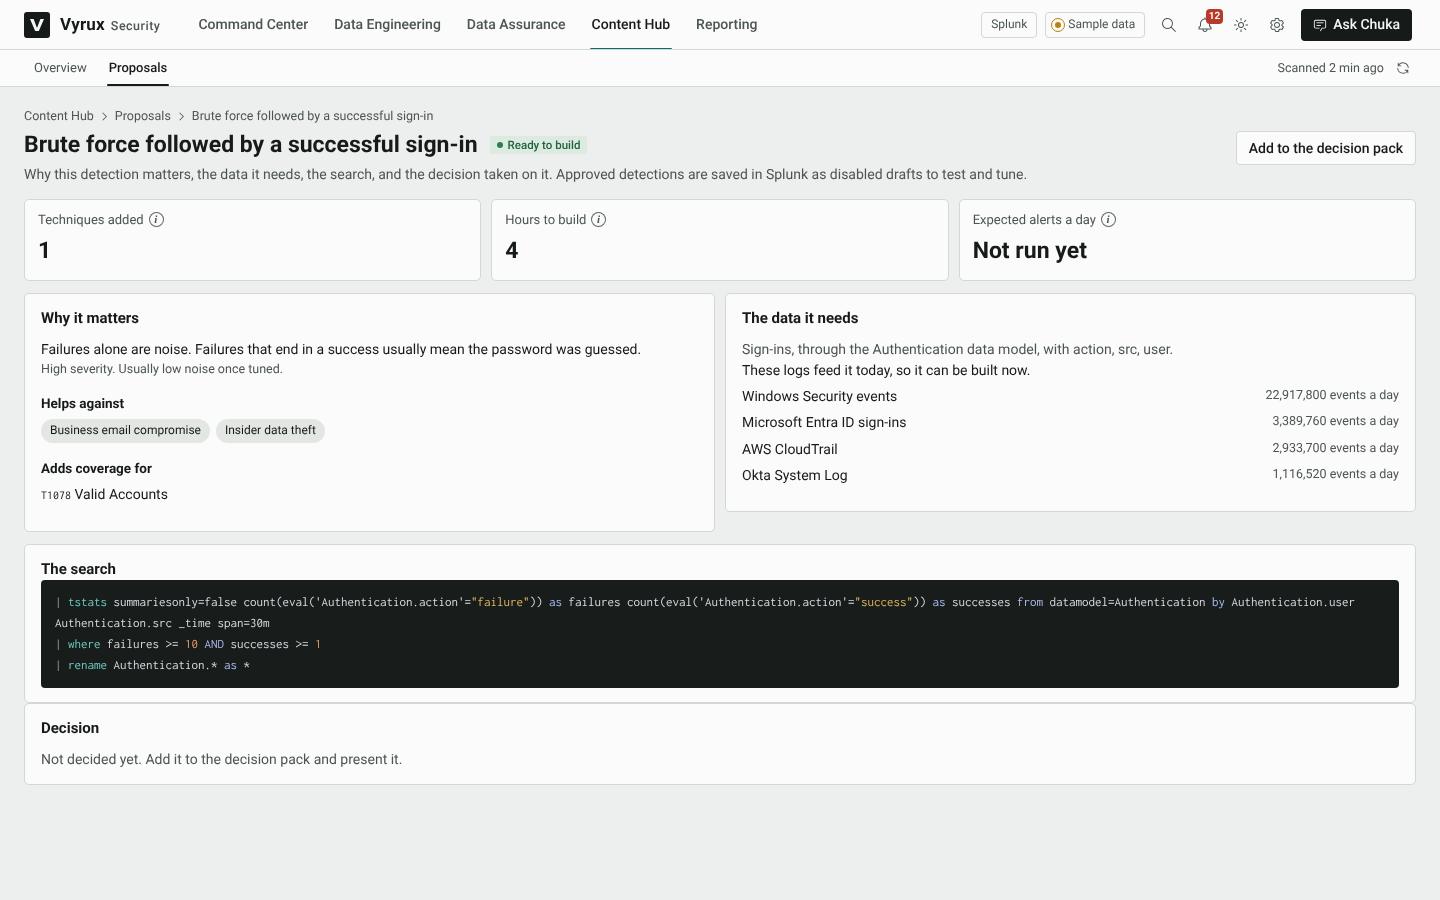
Every proposed detection with its severity, readiness, techniques and attack stories. Open one to see why it matters, the data it needs and the search itself. Add to pack puts it forward for the decision meeting.
The decision pack
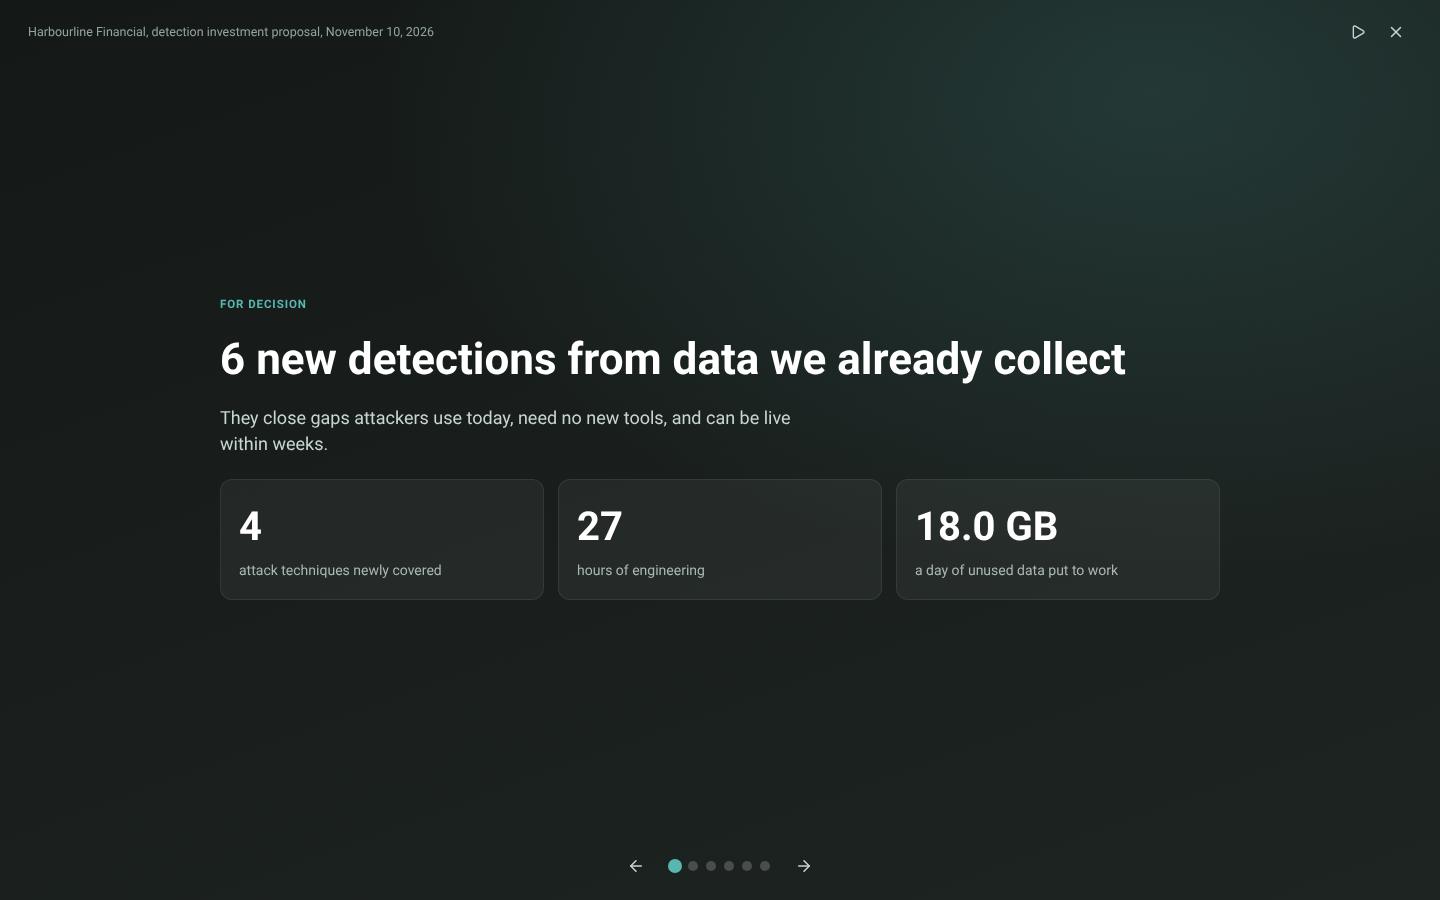
Present the decision pack opens a full-screen presentation for the approval meeting. Use the arrow keys to move between slides. Each decision is recorded with the name of the person who approved it, and approved detections are saved in Splunk as switched-off drafts to test and tune.