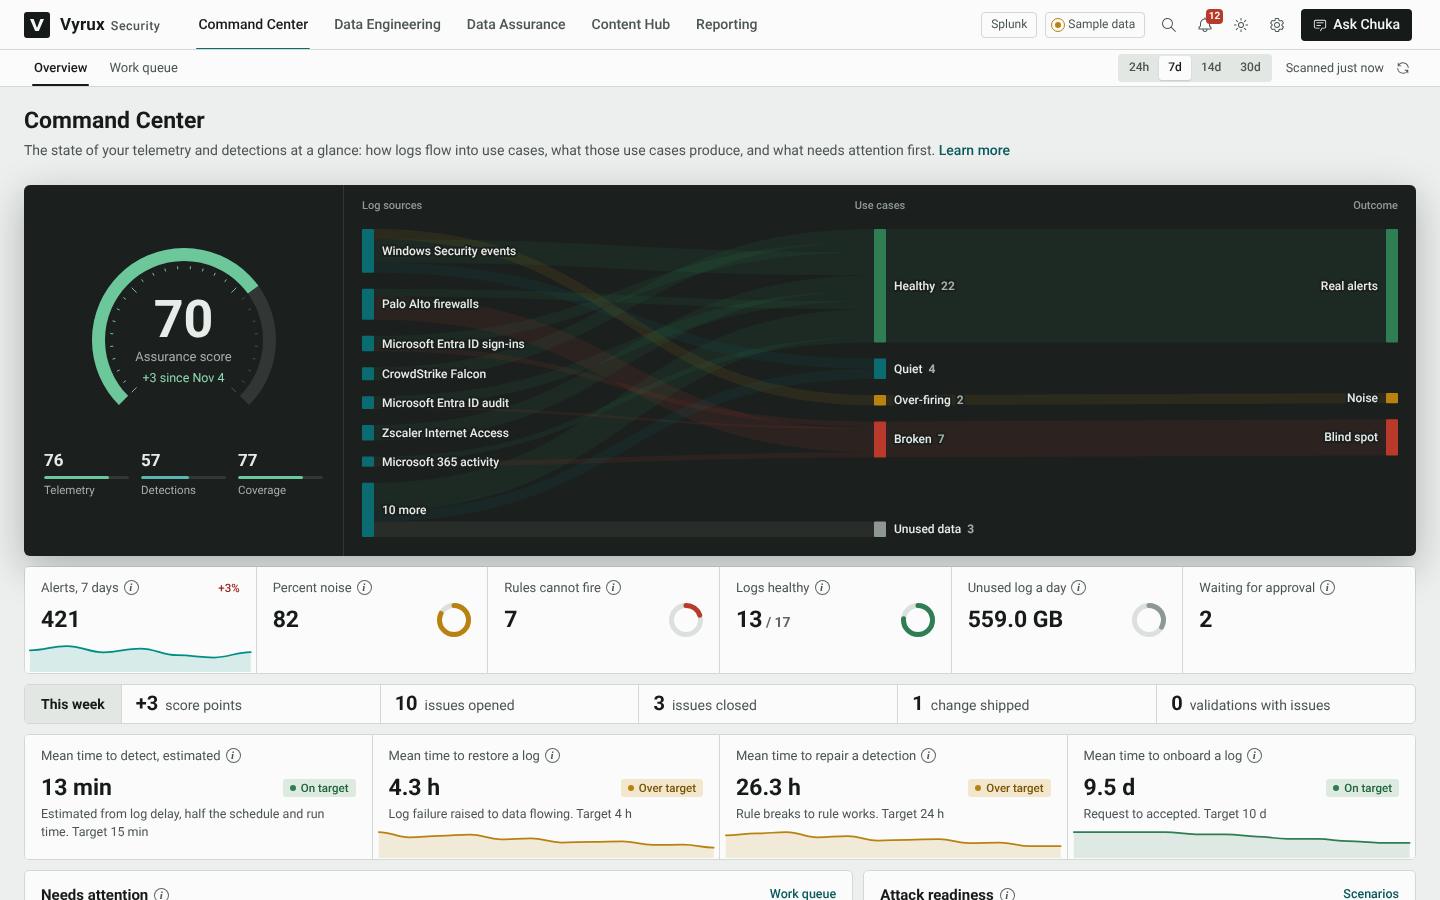
What Vyrux Security does
Vyrux Security checks that your Splunk logs arrive, that your detection rules can still fire, and that the alerts they raise are worth reading. It finds what is broken, explains it in plain words, and helps you fix it with an approval trail.
Most security teams find out a detection was blind only after an incident. A firmware update renames a field, a forwarder goes quiet, a macro is deleted, and a rule keeps running every five minutes while it can never match. Vyrux reads Splunk the way an auditor would and tells you, every 15 minutes, which logs and which use cases you can trust.
| Runs inside | Splunk Enterprise and Splunk Cloud, as a Splunk app |
| Reads | Your sourcetypes, saved searches, firing and run history, ingest volume, data models and forwarders |
| Changes | Nothing on its own. Every change to a rule, schedule or parser goes through approval and can be rolled back |
| AI agent | Chuka, which explains, reviews, fixes and tunes rules. Everything else works without it |
The five areas
-
The score, the flow from logs to alerts, and the work queue.
-
Every log: health, fields, parsing, onboarding, cost.
-
Every use case: can it fire, is it noisy, is it proven.
-
New detections your data already supports, ready for approval.
-
Posture, mean times, compliance evidence and the board pack.